Openai Report identifies malicious use of AI in cloud-based cyber threats
Openai's report identifies the misuse of artificial intelligence in cybercrime, social engineering, and impact manipulation. Targeting or operating specifically through cloud infrastructure. In “Confusion in Malicious Use of AI: June 2025”, the company outlines how threat actors weaponize large-scale language models for malicious purposes and how Openai is being pushed back.
The report highlights the growing reliance on AI by its enemies, expanding fraud, automating phishing, and deploying misinformation tailored to the platforms across Telegram, Tiktok, Facebook and more. Openai says it coordinates with cloud providers and global security partners to take action against criminals while using its own AI systems to combat these threats.
Three months after the previous update, the company said it had detected and destroyed activities, including:
- Cyber Operation Target cloud-based infrastructure and software.
- Social Engineering and Scam Scaling AI-assisted content creation.
- It affects impact operations You are trying to manipulate public discourse using AI-generated posts on platforms like X, Tiktok, Telegram, Facebook and more.
The report details 10 case studies in which Openai banned user accounts and shared findings shared with industry partners and authorities to enhance collective defense.
Here is how the company detailed tactics, techniques, and procedures (TTPS), as presented in the discussion of one representative case: Use ChatGPT to generate North Korea-related duties fraud operations and fake resumes and spoofing interviews.
| Activities | LLM ATT & CK Framework Category |
|---|---|
|
Automate and systematically manufacture detailed resumes tailored to various high-tech job descriptions, personas and industry norms. Threat actors automate the automatic generation of consistent work history, educational backgrounds, and references via loop scripts. |
LLM supported social engineering |
|
Threat actors used the model to answer employment-related application questions, coding assignments, and real-time interview questions based on a specific uploaded resume. |
LLM supported social engineering |
|
Threat actors sought guidance on remotely configuring corporate-issued laptops to be located domestically, including advice on geographic masking and how to avoid security for endpoints. |
Avoid detection of LLM enhanced abnormality |
|
LLM will awaken your computer remotely to help you code tools to move your mouse automatically or to help you set up a remote working infrastructure. |
LLM supported development |
Openai's report outlines multiple campaigns that go beyond employment fraud cases, including threat actors who abuse AI in cloud-centric and infrastructure-based attacks.
Cloud-centered threat activity
Many OpenAI campaigns have expanded their impact using targeted cloud environments or cloud-based platforms.
- Russian-speaking groups (operation) Scopecreep) CHATGPT was used to help with iterative development of sophisticated Windows malware distributed via Trojanized gaming tools. The campaign leveraged a cloud-based GitHub repository for malware distribution and used a telegram-based C2 channel.
- Chinese groups (Keyhole Panda and Vixen Panda) used ChatGPT to support AI-driven penetration testing, qualification harvesting, network reconnaissance and automating the impact of social media. Their goals included the US federal defense industry network and government communications systems.
- Dubbing operation Spam UncleIt is also linked to China, using AI to polarize US political content and pushed it through X and Bluesky social media profiles.
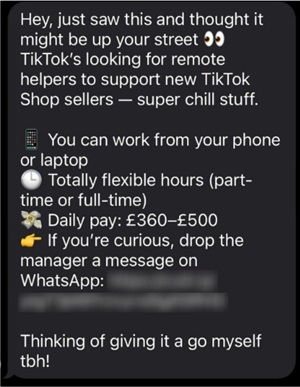
- The wrong numberpossibly based in Cambodia, using AI-generated multilingual content to carry out task fraud via SMS, WhatsApp, and Telegram, seducing victims into a cloud-based crypto payment scheme.
[Click on image for larger view.] The SMS was randomly sent to OpenAI investigators generated using ChatGPT. (Source: Openai).
Defensive AI works
Openai says it uses AI as a “power multiplier” for its research team, allowing it to detect large-scale abusive activity. The report also highlights how to use AI models to paradoxically expose malicious actors by providing views to workflows.
“AI research is an evolving discipline,” the report states. “All surgeries that we disrupt will allow threat actors to better understand that they are trying to exploit our model and improve our defense.”
The company is looking for continuous collaboration across the industry, noting that AI is just a part of the broader Internet security ecosystem. AI is just a part of the broader Internet security ecosystem.
For cloud architects, platform engineers and security professionals, reports are useful readings. It shows not only how attackers use AI to speed up traditional tactics, but how cloud-based services are central to both goals and modern threat campaign infrastructure.
The full report is available on the OpenAI site.
About the author
David Ramel is the editor and writer of Converge 360.