European Commission Headquarters in Brussels. (Credit: Ferdous Al-Faruque)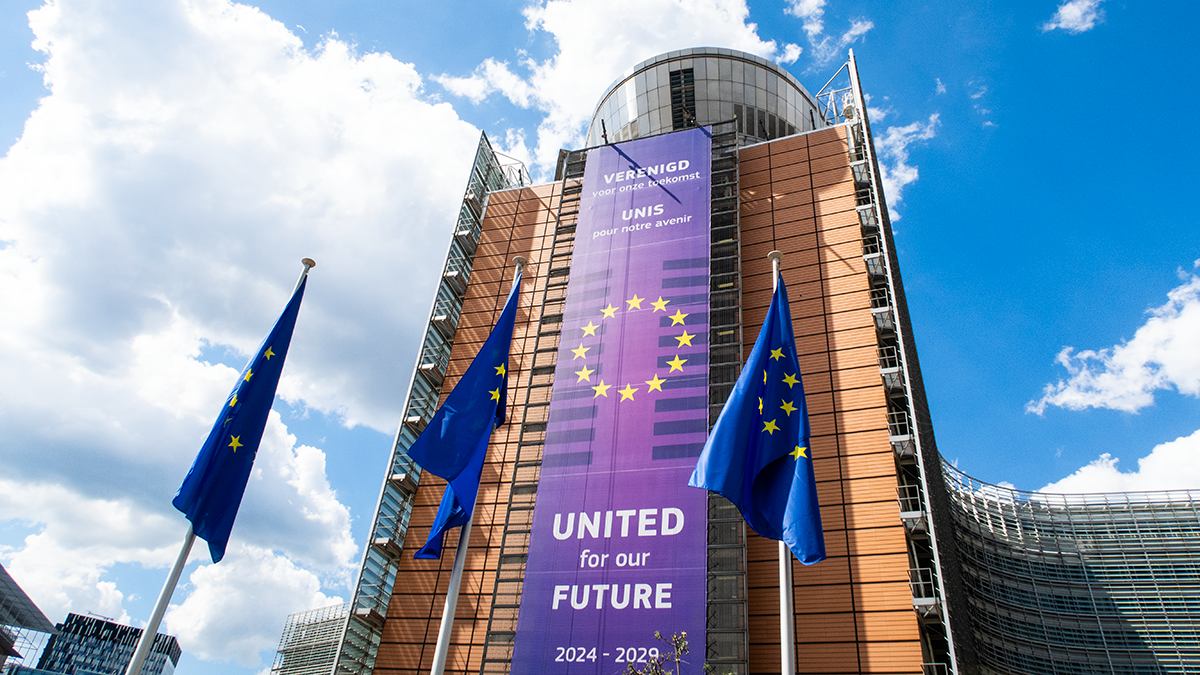
The European Commission on Monday published new guidelines to help providers and implementers of artificial intelligence (AI) systems meet their transparency obligations under EU AI law, including examples of exceptions to these requirements. Although not specific to healthcare products, companies developing healthcare products with AI system components may be subject to transparency rules.
The guidelines specify the responsibility of AI providers and adopters to inform users when interacting with AI systems and to ensure that content generated or manipulated by AI is reliably identifiable under section 50 of the AI Act. The AI Act will come into force on August 2, 2024, and the transparency provisions will come into force on August 2, 2026.
“With today’s guidelines, the European Commission supports the smooth and effective application of AI law to increase the transparency and trust of AI systems and content that interact with people, such as chatbots and AI agents. These guidelines will help providers and adopters meet their obligations under AI law, while also helping citizens know when they are interacting with AI,” announced Hena Virkunen, Executive Vice-President for Technology Sovereignty, Security and Democracy at the Commission.
According to a Commission press release, “Transparency obligations help people recognize when they are interacting with AI and when content has been generated or modified by AI, reducing the risk of deception and manipulation. The guidelines published today clarify which providers and implementers must comply with transparency obligations for the marking and labeling of conversational AI systems and AI-generated content.”
According to a press release, the guidelines clarify several important concepts and provide exemptions and examples from the law. These concepts include directly interactive AI systems such as chatbots, as well as synthetic content, including both partially and fully AI-generated text, deepfakes, and AI-generated text on topics of public interest.
According to the release, the guidelines require providers to design AI systems so that individuals are explicitly notified whenever they directly interact with an AI system. It should also include machine-readable markers to facilitate detection of AI-generated or manipulated content.
Organizations deploying AI systems must notify individuals if they are exposed to emotional recognition and biometric classification tools, deepfakes, and public interest text publications that lack human review or editorial control, unless they meet certain exceptions such as obviousness.
Transparency requirements are separate from the AI Act’s risk classification system and compliance with section 50 does not affect other obligations for high-risk systems under Chapter 3 of the Act.
However, the Guidelines state that the transparency requirement under Article 50(1) may be waived if it is clear that the interaction with the system is artificial. For example, certain systems intended to be used only by trained medical professionals to support medical diagnosis and suggest potential treatments are excluded from Article 50(1) for truism.
AI system developers may be exempt from the transparency requirements under Article 50(2) if their AI system only makes standard edits or minor changes. For example, the guidelines state that “technical processing or reconstruction of medical images within a medical device” such as annotations, boxes, contours, circles, and heatmaps are exempt from the transparency rules.
Guidelines, press releases; announcements